 1 hour ago
2
Ethereum’s next big upgrade is supposed to make the network better. Lido’s head of engineering thinks it could also briefly make it easier to steal stakers’ ETH. On October 20, 2026, Dima Gusakov, Head of Engineering at Lido Finance, publicly flagged a potential front-running attack. The risk targets delegated staking protocols during the transition to the Glamsterdam hard fork. The window is narrow, but the stakes involve the deposits that make liquid staking work. How the attack would work Glamsterdam introduces builder deposits that use a specific type of withdrawal credentials, marked with the 0xB0 prefix. Withdrawal credentials essentially tell the network who owns the staked ETH and where it ultimately goes. According to Gusakov’s warning, builder deposits and validator deposits will run through shared deposit queues around the fork. That overlap creates an opening. A malicious node operator with the right access could submit a builder deposit that preemptively claims ETH meant for a staker’s validator. The result, if the attack succeeds: the deposit gets credited to the attacker’s builder account. The validator the staker was funding never activates. The vulnerability is spe...
Related

Bitcoin Price Forecast: MSCI Decision Could Impact BTC USD P...
13 minutes ago
0
JPMorgan projects Bitcoin to outperform US stocks and gold o...
17 minutes ago
0
Saudi-led coalition intercepts Houthi missile targeting Riya...
24 minutes ago
0
Sophon to shut down mainnet on November 30, sets earlier wit...
30 minutes ago
0
MrBeast linked firm files trademarks covering crypto exchang...
38 minutes ago
0
FX market tightens AI governance as autonomous trading sprea...
38 minutes ago
0
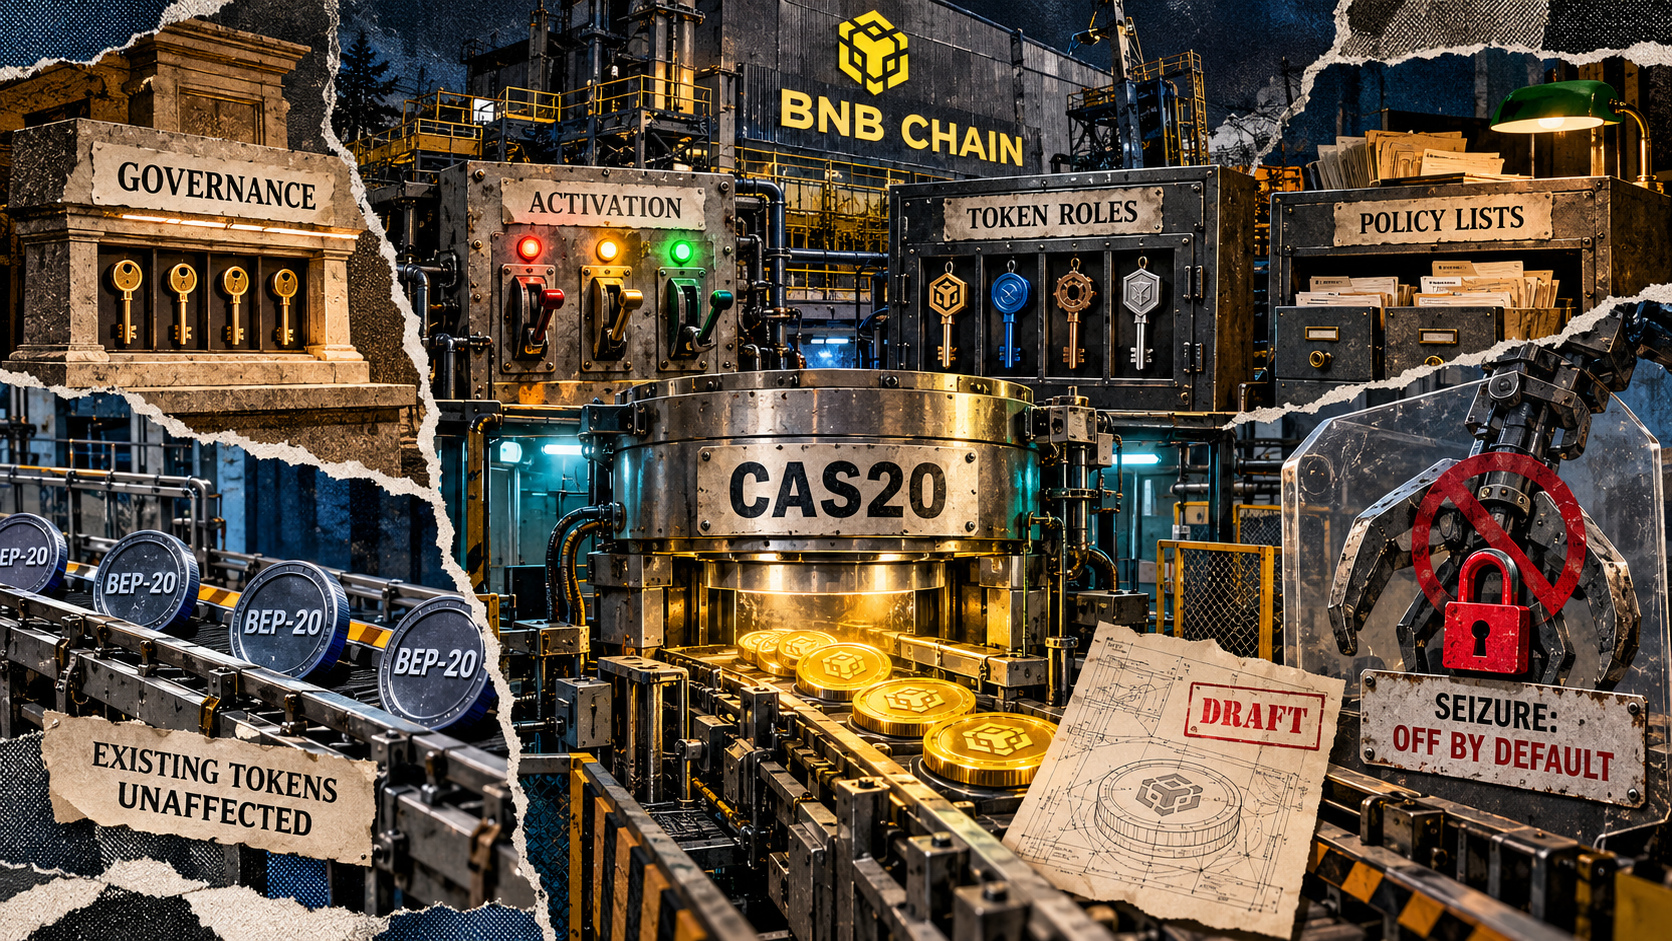
BNB Chain splits asset power across 4 roles while admins hol...
51 minutes ago
0
BlackRock files for third Bitcoin ETF, still no Solana or XR...
58 minutes ago
0
Popular
XRP Ledger Explained: How the Network Behind XRP Works
4 weeks ago
39
Grayscale’s Zcash ETF files for 3-for-1 forward share split
4 weeks ago
39
 English (US) ·
© Clint's Cryto News 2026. All rights are reserved
