 1 day ago
3
Phishing has been a problem for decades. What’s new is that it now comes with a subscription tier and an AI content generator, and the people running it were apparently operating out of the UK until last week. Microsoft’s Digital Crimes Unit announced on September 22 that it had dismantled the core infrastructure behind EvilTokens, a phishing-as-a-service platform the company tracks internally as Storm-2992. The operation compromised more than 12,000 Microsoft 365 inboxes across over 10,000 organizations globally before Microsoft and its partners shut it down. Two UK administrators, aged 32 and 38, were arrested in coordination with Health-ISAC, cybersecurity firm SpyCloud, and local law enforcement. Both suspects were subsequently released on bail while investigations continue. How EvilTokens actually worked The clever part of EvilTokens was that it didn’t try to trick victims into handing over passwords. It exploited Microsoft’s own device authorization grant flow, the legitimate OAuth process that lets users authenticate on devices without keyboards, like smart TVs. A victim would receive a phishing message directing them to a real Microsoft page and asking them to enter a devic...
Related

Zuckerberg to unveil new AI products as Meta’s Muse app tops...
28 minutes ago
0
Treasury 5-year yield surges 15 basis points as markets brac...
29 minutes ago
0
$425M in crypto long positions liquidated amid market correc...
32 minutes ago
3
Renishaw reports record results amid AI chip demand surge
36 minutes ago
0
Base financing markets grow 133% this year, driven by Morpho...
41 minutes ago
0

Wall Street falls as oil rebounds amid Middle East tensions
42 minutes ago
0
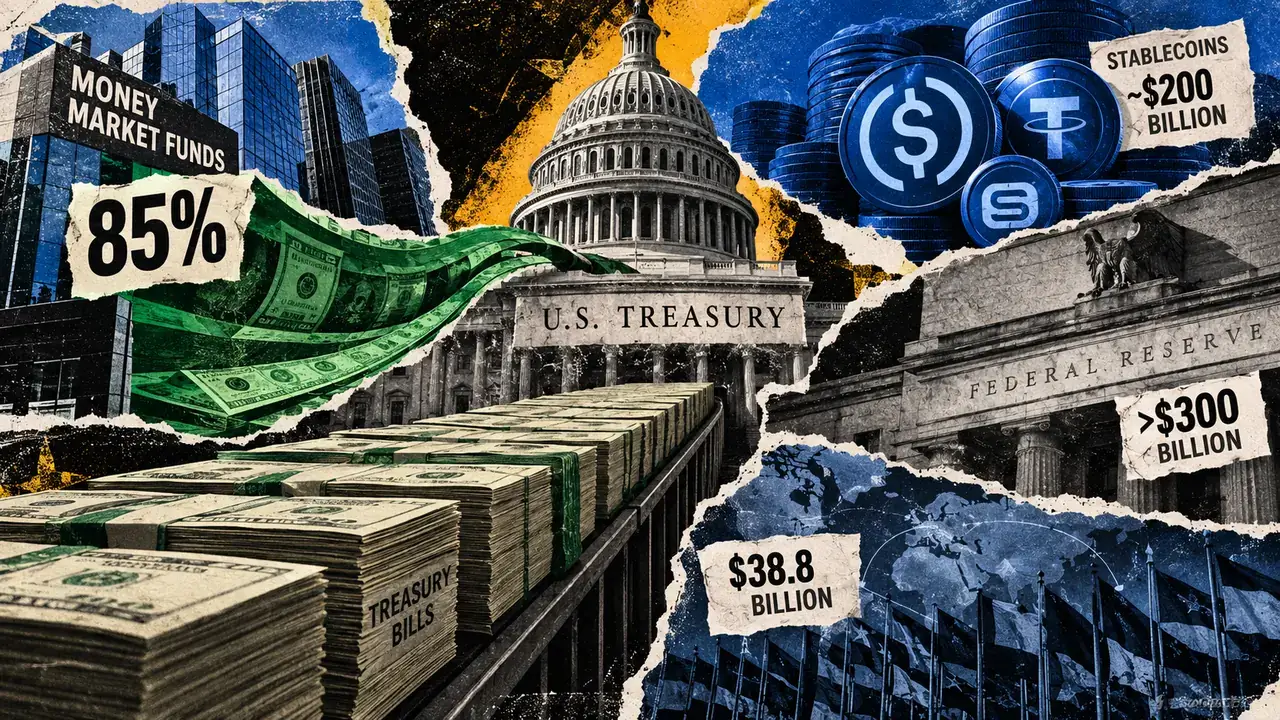
Stablecoins hold nearly $200 billion in US debt, but money f...
44 minutes ago
0
Microsoft commits $15.2 billion to UAE as Middle East AI pus...
46 minutes ago
0
Popular


Starknet shields 45 assets with new privacy framework
2 weeks ago
61



 English (US) ·
© Clint's Cryto News 2026. All rights are reserved
